- Concept
- Version · 6.0.2
- Manage
Signing in with single sign-on
Last updated: November 17, 2026
When your workspace uses Microsoft Entra single sign-on, people sign in with their work Microsoft account instead of a password. Here's what they see along the way.
What users see on the sign-in page
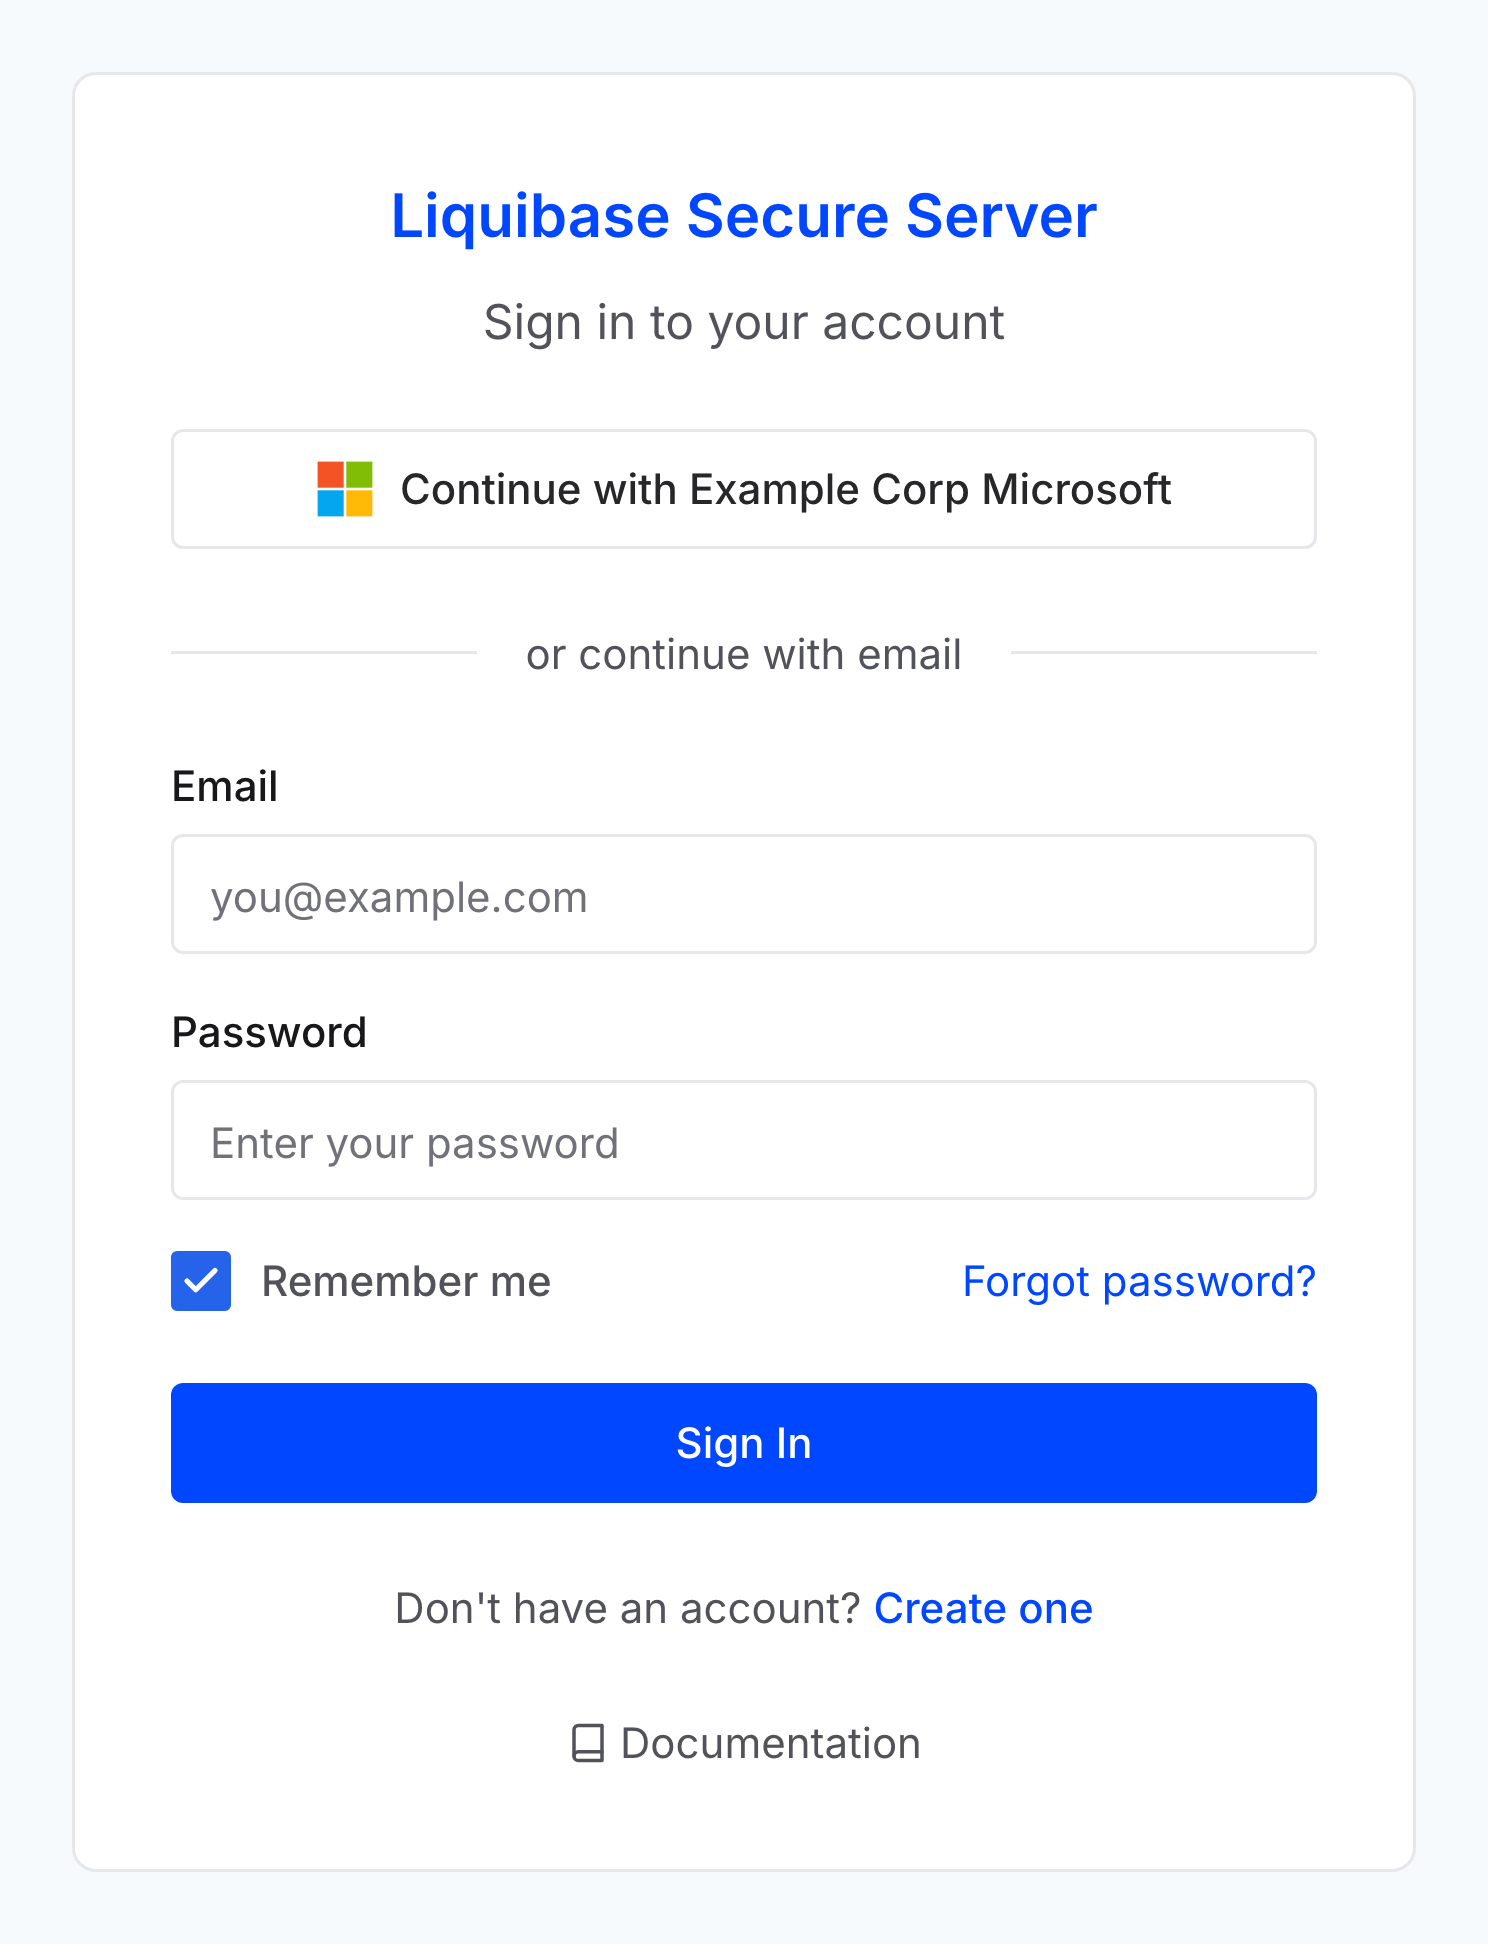
When single sign-on is enabled, a button appears on the sign-in page reading Continue with followed by the display name the administrator configured, such as Continue with Acme Corp Microsoft.
The button looks and behaves the same whether the workspace uses OpenID Connect or SAML 2.0. That is deliberate, and it means there is one sign-in path to describe rather than two.
When single sign-on is disabled, the button disappears entirely, which reads to a user as the option vanishing rather than a setting being off.
Sign-in is restricted to your tenant
Only users in the configured Microsoft Entra tenant can sign in. Personal Microsoft accounts cannot.
This matters most to someone holding more than one Microsoft identity, such as a consultant with both a client account and their own. They must sign in with the identity that belongs to the configured tenant.
What happens on first sign-in
A user signing in through single sign-on for the first time has an account created from the email claim. What happens next depends on whether an administrator invited them.
Invited users join the groups named in their invitation and can start working straight away. The invitation must be for the address the identity provider sends, and it must not have expired.
Everyone else is added to the Pending group and has no permissions until an administrator moves them.
For someone who was not invited, this is the single most confusing moment in the whole path, because the sign-in succeeds and the application is empty. That is correct behavior, and it looks exactly like a broken login.
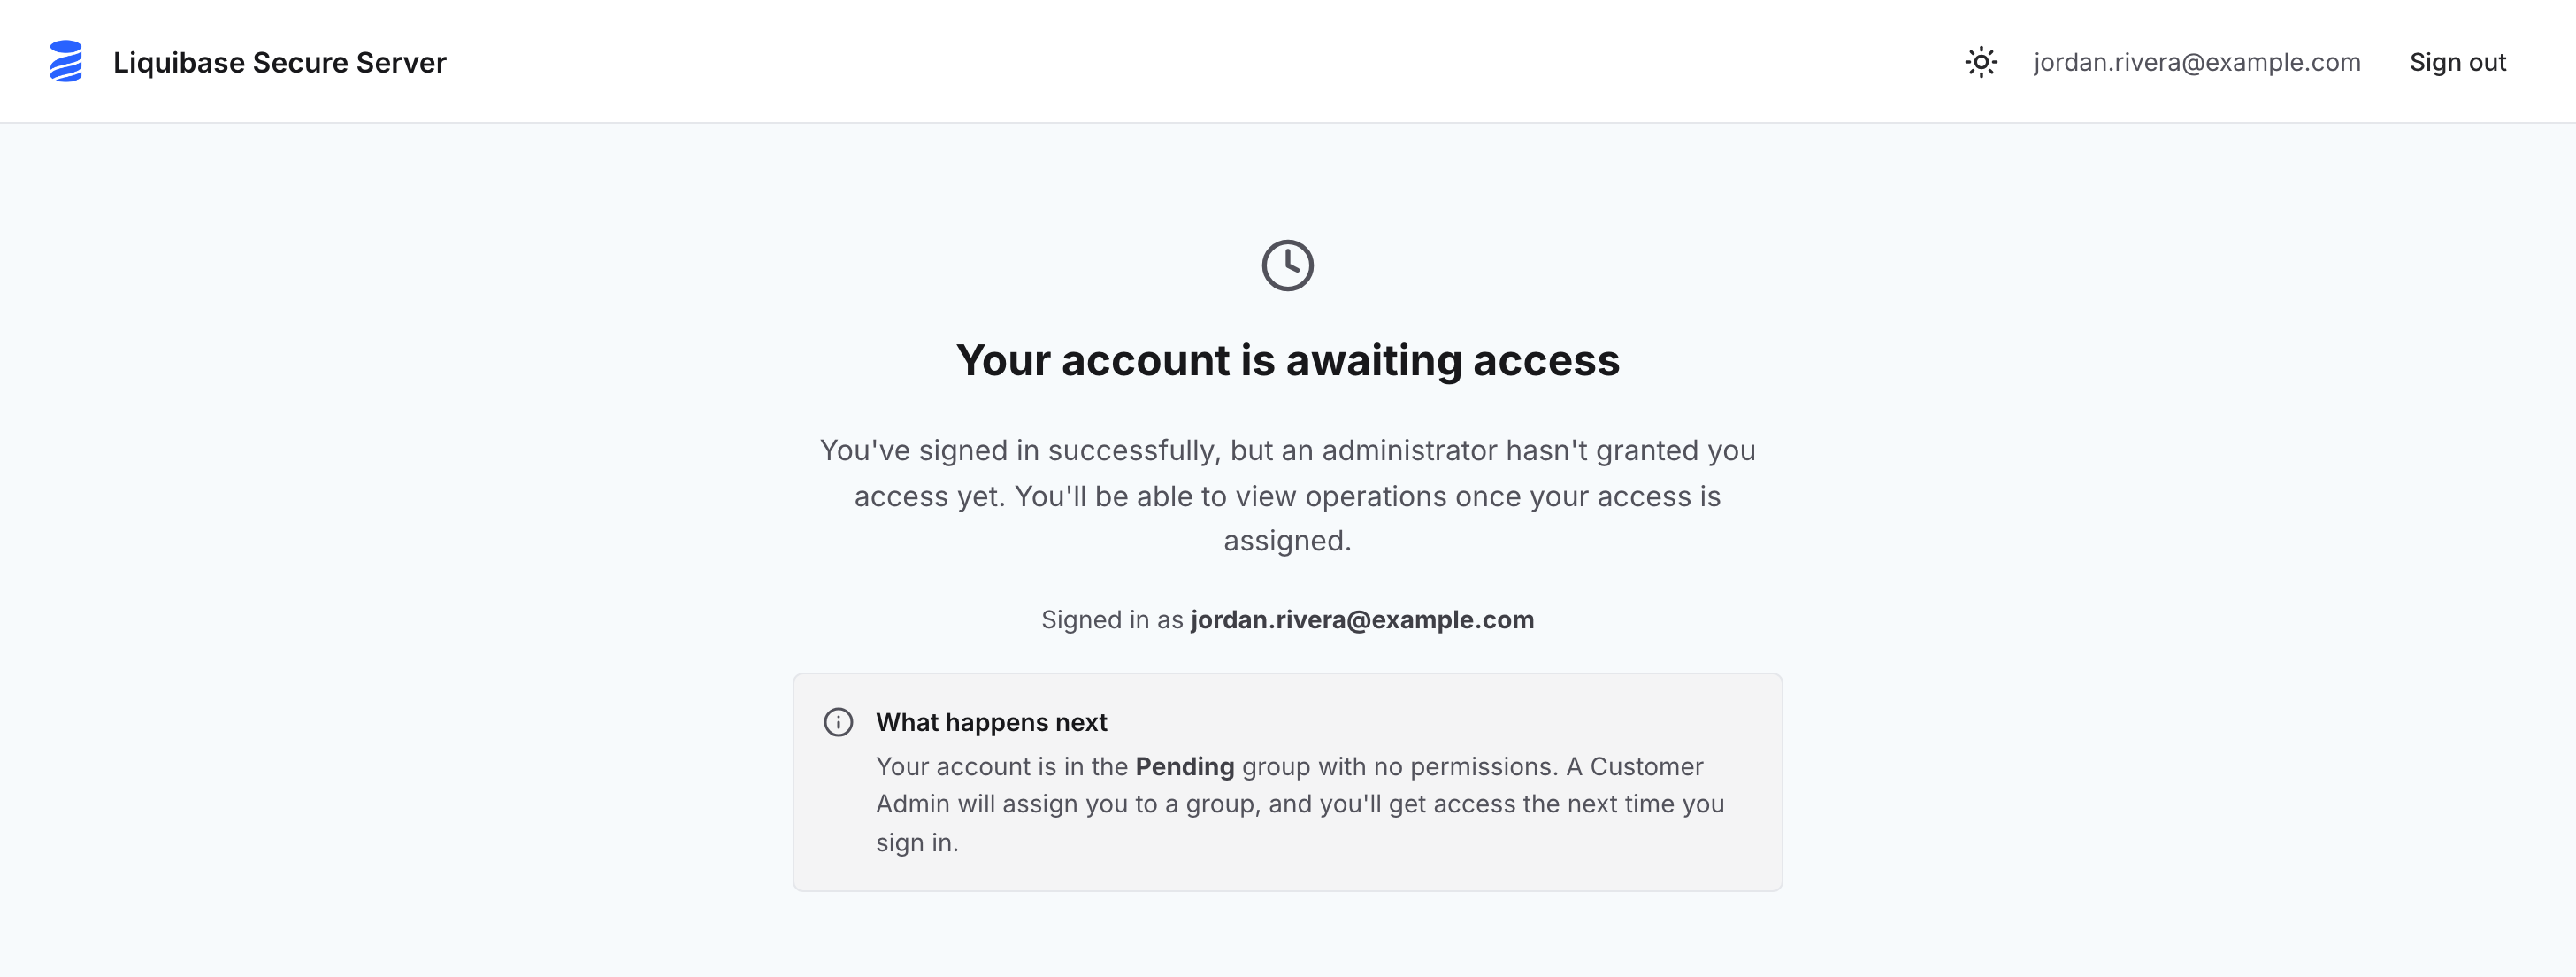
The user sees a screen headed Your account is awaiting access, telling them they signed in successfully but an administrator has not granted them access yet, along with the address they signed in as and a Sign out action.
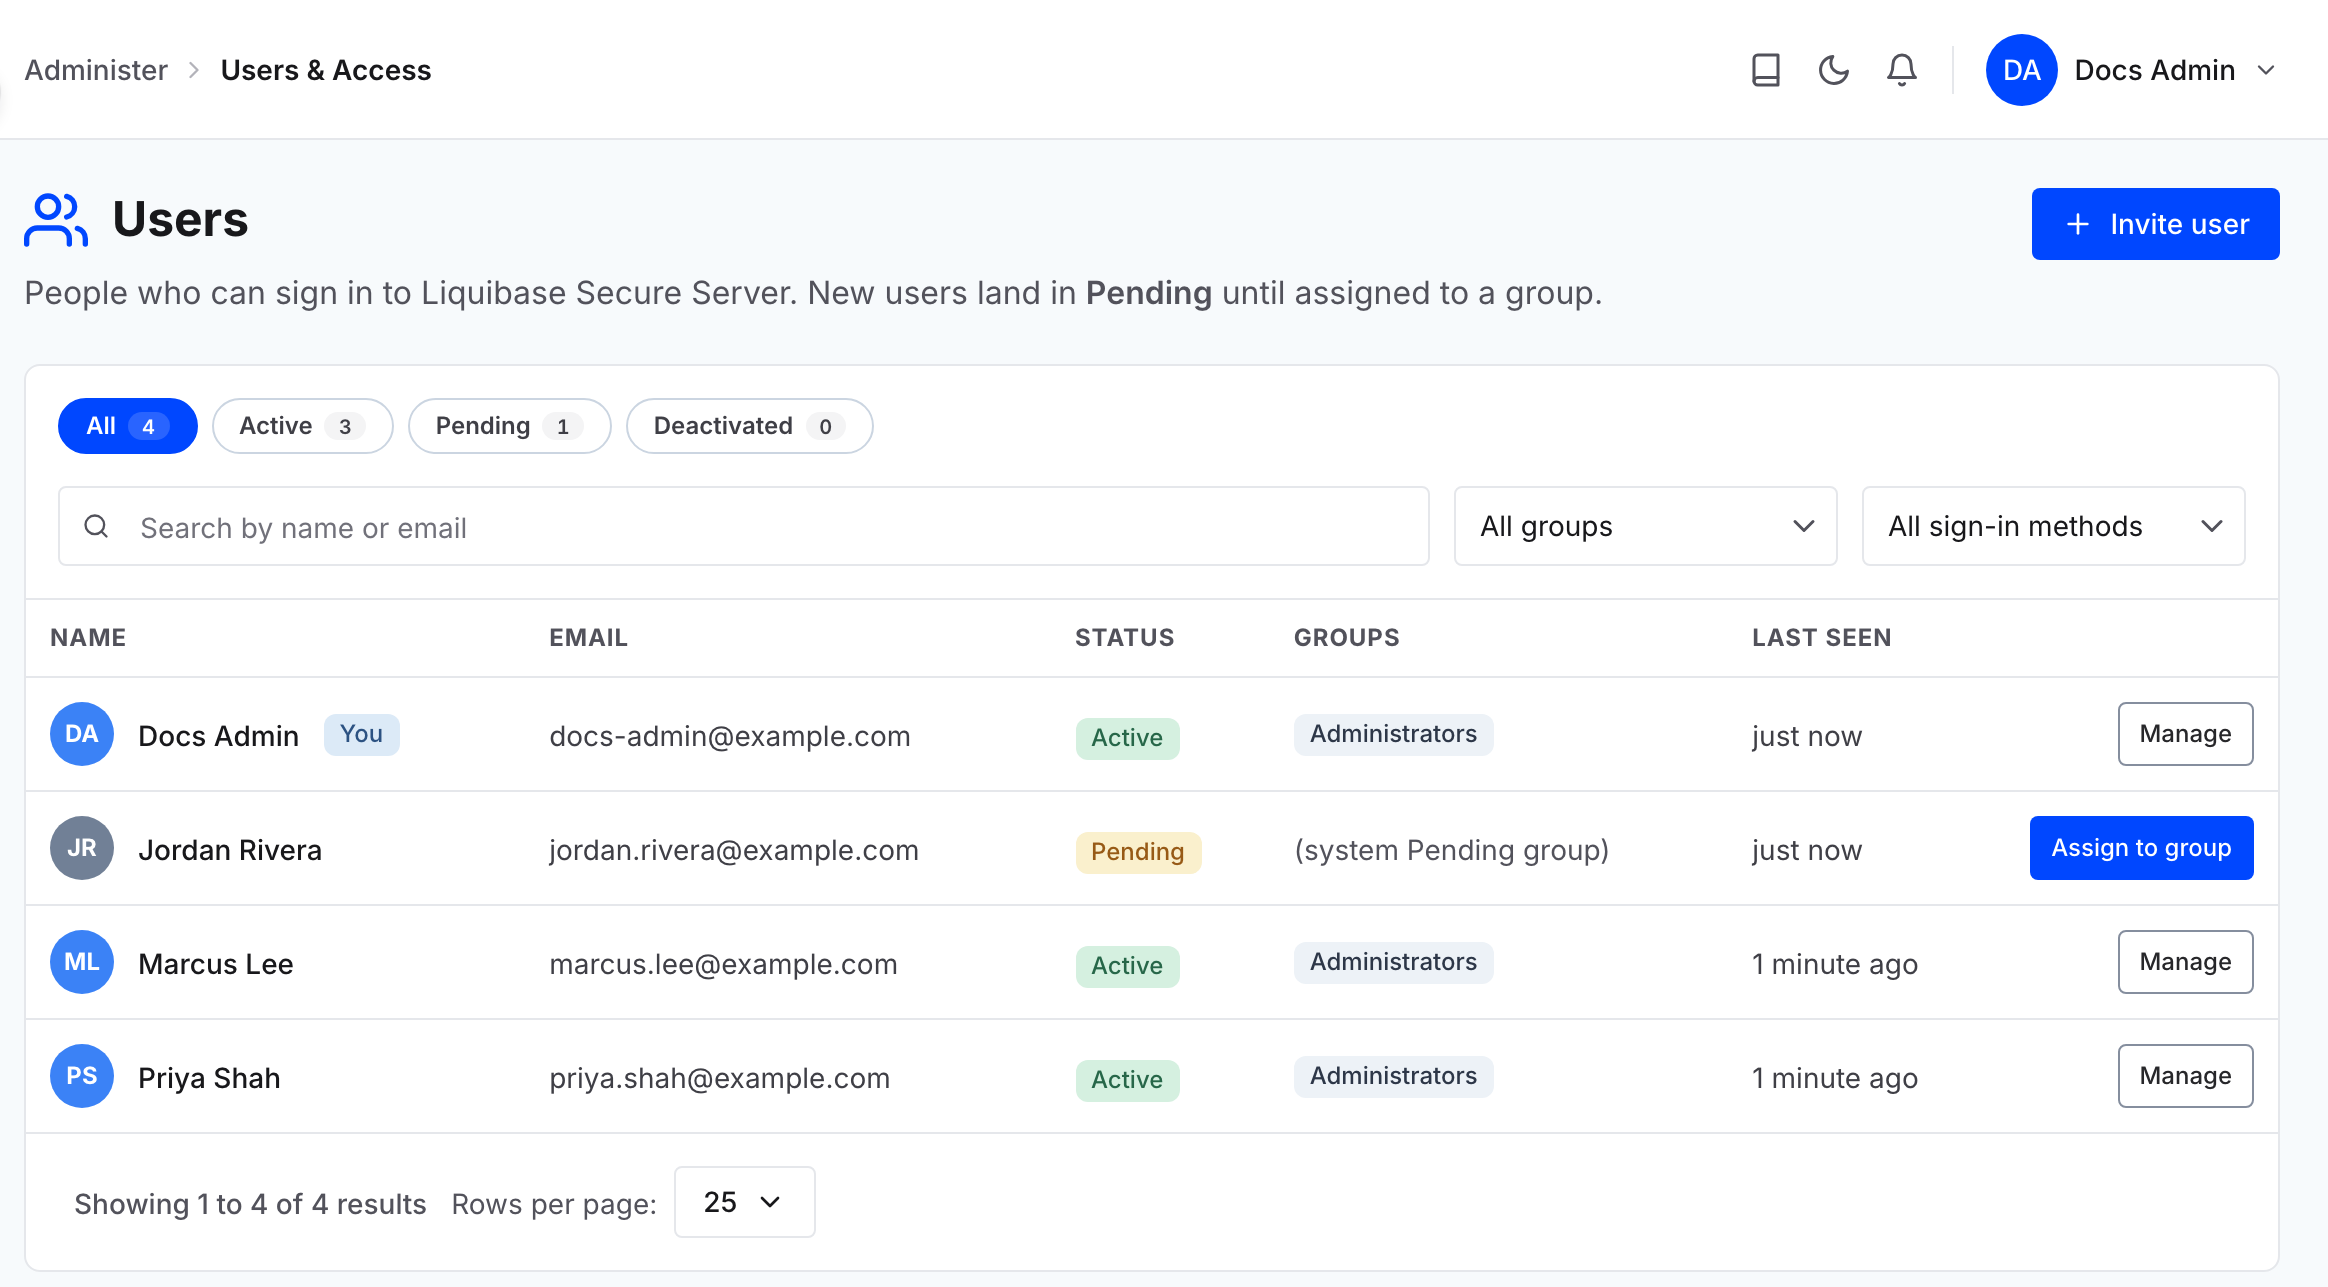
An administrator resolves it by assigning them to a group. See Invite and manage users.
Liquibase Secure does not use the groups your IT team manages in Microsoft Entra, such as a Database Administrators group. Access comes only from groups in Liquibase Secure, either named in an invitation or assigned by an administrator.
Single sign-on and passwords coexist
Enabling single sign-on does not disable password sign-in. Both paths stay on the sign-in page.
Both are needed. The first administrator has to be able to sign in before single sign-on exists, and workspaces without single sign-on keep using passwords.
A user has exactly one identity, either single sign-on or password. There is no linking or merging of the two, so an account created with a password does not become a single sign-on account because the same person later signs in through the identity provider.
Multi-factor authentication comes from your own identity provider. Liquibase Secure does not offer two-factor authentication of its own, so enforce it in Entra.
Closing the instance to new accounts
An administrator can close self-service registration on the Authentication page, which closes the create-account path. See Manage authentication settings.
Note: This is not a single sign-on only mode. Password sign-in keeps working, and only account creation closes. The distinction is deliberate, so that an instance cannot be locked out from its own sign-in page.
Troubleshooting
If a sign-in doesn't work, Troubleshoot single sign-on walks through the most common problems and how to fix each one.